🔍 IAM Access Analyzer for S3 — Simplified
A security feature that automatically scans your S3 buckets to flag ones that are publicly accessible or shared with other AWS accounts — so you can catch unintended access before it becomes a problem.
💡 Exam Tip: It identifies buckets that are public or shared with other accounts, helping you catch and fix unintended access.
🔍 What Is It?
Rather than manually combing through bucket permissions, this tool automatically reviews your S3 access settings and surfaces any buckets that might be exposed — checking that only the people and accounts you actually intended can get in.
⚙️ How It Works
It inspects everything that controls bucket access:
📄 Bucket Policies
🔑 Access Control Lists (ACLs)
📍 Access Point Policies
From there, it works out exactly who can reach your data.
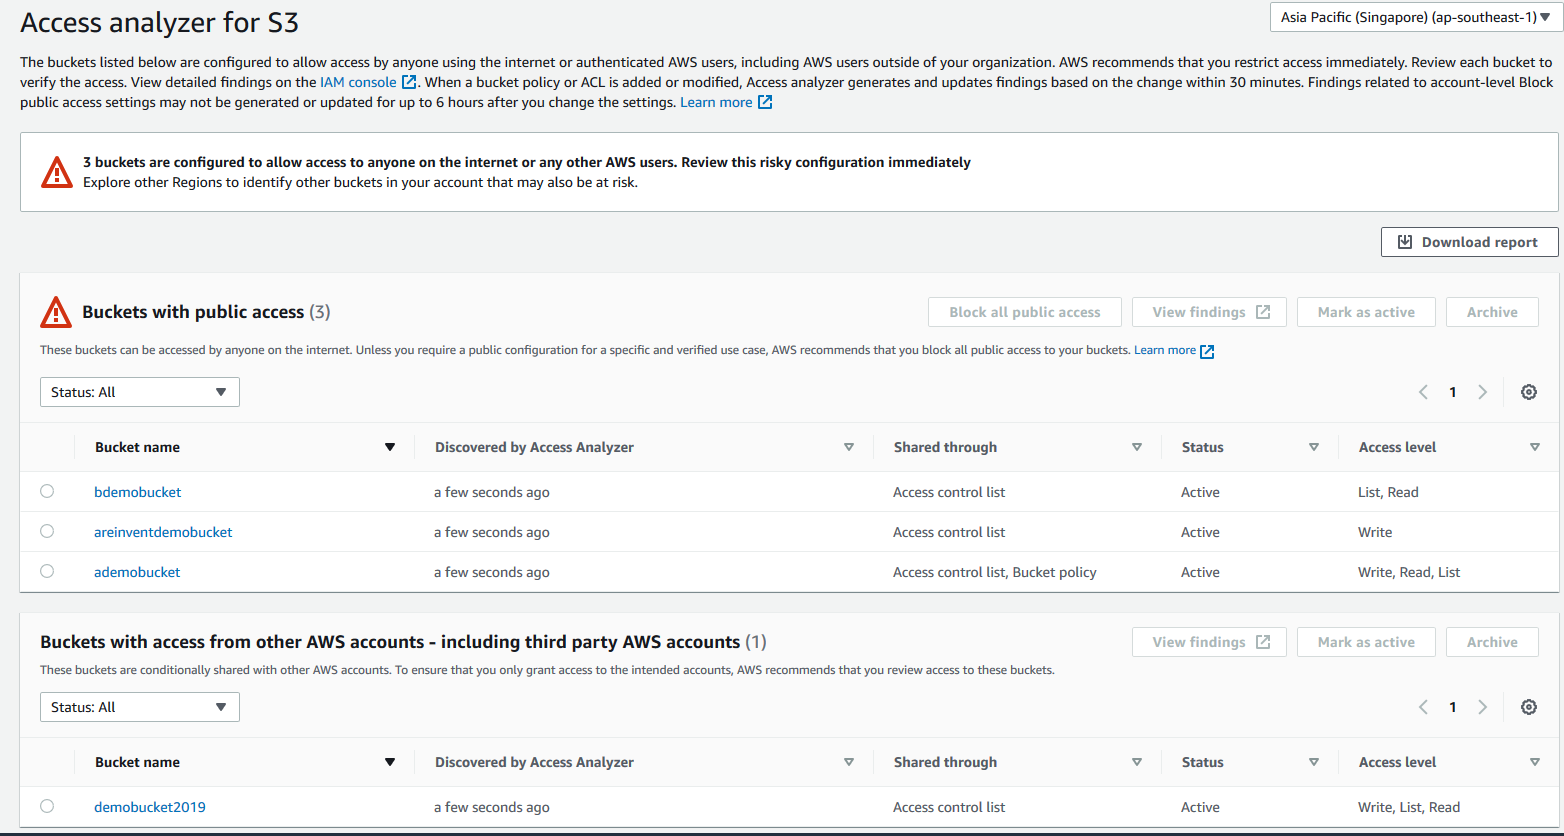
🚨 What It Catches
It flags buckets that are:
🌍 Open to the public internet
🤝 Shared with other AWS accounts
⚠️ Accessible in ways you may not have intended
That means potential risks surface early — before they turn into real problems.
🛡️ Why It Matters
Once findings appear, you review each one and decide if the access makes sense:
✅ Deliberately shared with a partner account? No action needed.
❌ Accidentally public, or shared with an unknown account? Time to fix it.
This keeps your buckets locked down to exactly who's supposed to have access.
🔗 Under the Hood
Amazon S3 uses IAM Access Analyzer behind the scenes.
IAM Access Analyzer is an AWS service that helps identify resources in your AWS account that are shared with external entities, such as:
Other AWS accounts
Public users
External organizations
For Amazon S3, it focuses specifically on identifying buckets that may have unintended access.